PortfolioAI Security

AdrianInfantes

AI Security Architect

About

I'm an AI Security Architect with nine years in machine learning and AI, from data science and production ML to securing agentic systems. I design guardrail platforms, protected agent runtimes, and evidence-led release paths for LLM agents and RAG copilots on AWS, and I test them the way an attacker would.

Architecture folio / Plates 01–05

AWS Architect

Five AWS architectures for controlled, observable AI systems. Explore each problem, decision, and limitation in an interactive map.
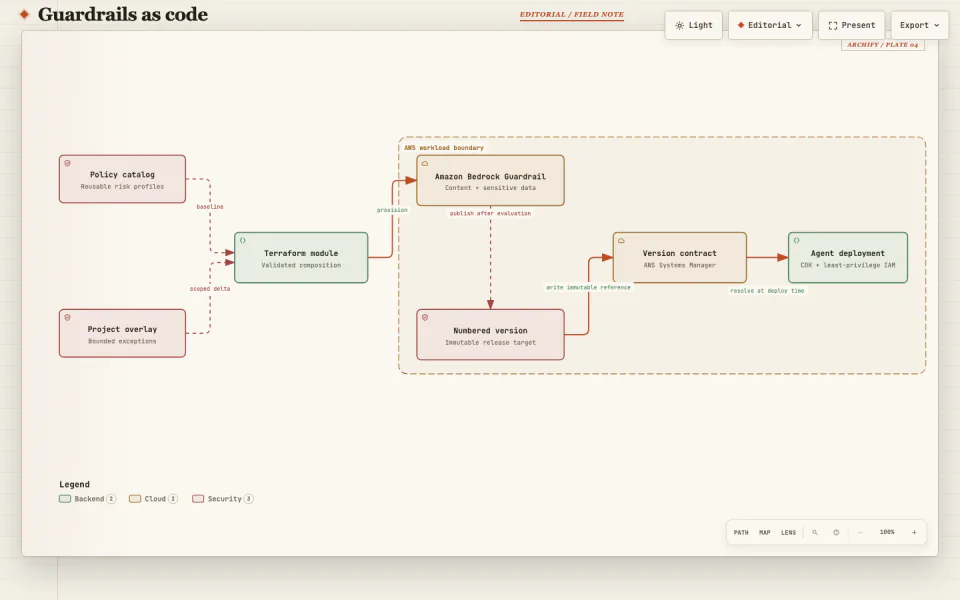
  1. Architecture preview for reusable guardrail profiles, Terraform delivery, and a versioned SSM contract

    Guardrails as code

    Problem
    Teams need consistent guardrail policies and an explicit version for each application to use.
    Decision
    Define reusable profiles in Terraform and publish a versioned reference through SSM.
    Limitation
    Provisioning a policy does not prove its effectiveness or that an application applies it. Both need separate checks.
    Technical scope
    Amazon Bedrock Guardrails, Terraform, versioned SSM contract
    Explore interactive map
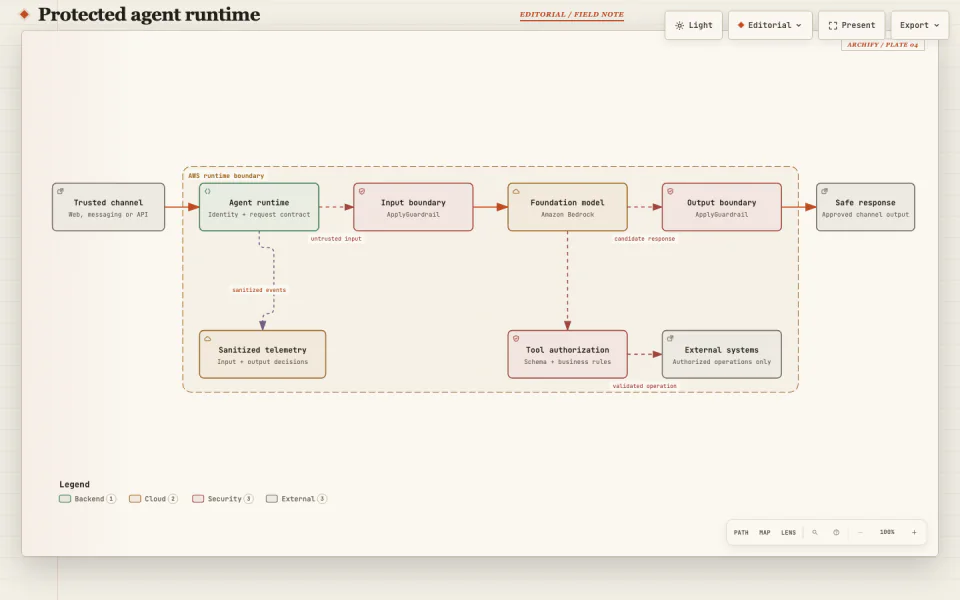
  2. Architecture preview for input and output protection, Bedrock invocation, and a deterministic tool boundary

    Protected agent runtime

    Problem
    Model inputs and outputs need protection while tool permissions remain under application control.
    Decision
    Apply input and output checks around Bedrock, with deterministic authorization before tool execution.
    Limitation
    Guardrails assess content; they do not grant permission to use tools or access data.
    Technical scope
    Amazon Bedrock, Bedrock Guardrails, IAM, deterministic tool boundary
    Explore interactive map
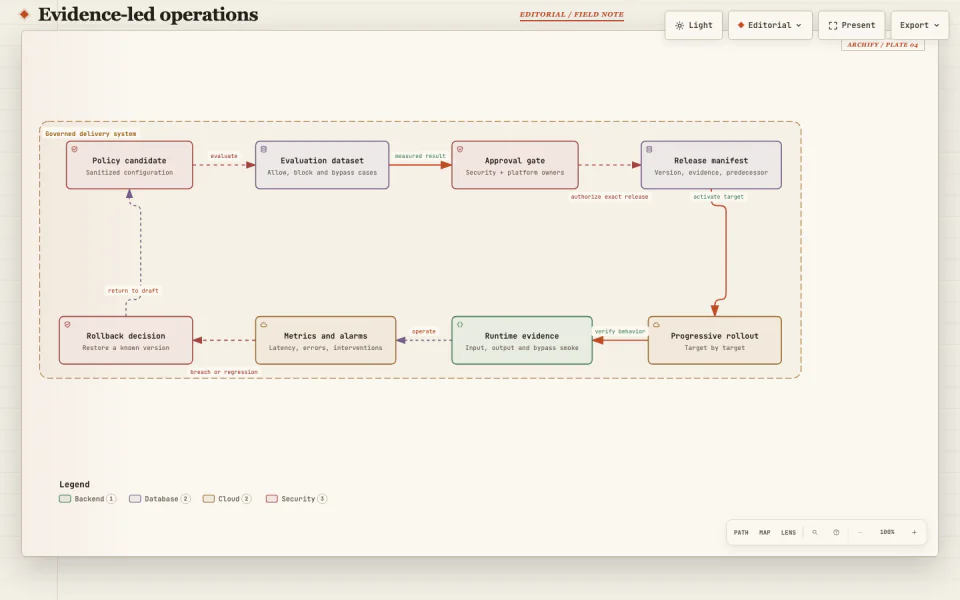
  3. Architecture preview for evaluation gates, payload-free telemetry, progressive rollout, and rollback

    Evidence-led operations

    Problem
    AI releases need evidence for promotion and clear signals for rollback without logging sensitive payloads.
    Decision
    Combine evaluation gates and telemetry without payloads with progressive release and explicit rollback.
    Limitation
    Release quality depends on evaluation coverage and chosen thresholds. Telemetry alone cannot demonstrate safety.
    Technical scope
    Evaluation gates, CloudWatch, progressive rollout, rollback
    Explore interactive map
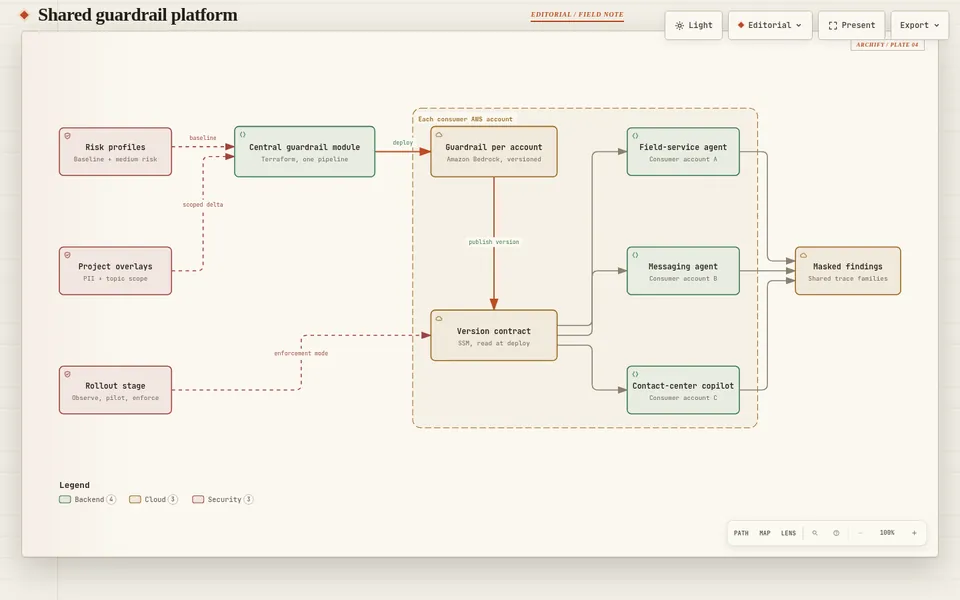
  4. Architecture preview for a central guardrail module deployed to consumer accounts, a versioned SSM contract, and masked findings

    Shared guardrail platform

    Problem
    Agent teams in separate AWS accounts need the same content controls without rebuilding them in every project.
    Decision
    One Terraform pipeline deploys a versioned guardrail to each consumer account and publishes its contract in SSM. Agents resolve it at deploy time while enforcement moves from observe to pilot to enforce.
    Limitation
    A shared baseline cannot fit every use case. Project overlays need their own evaluation, and enabling enforcement does not prove that every consumer applies it.
    Technical scope
    Amazon Bedrock Guardrails, Terraform, multi-account SSM contract, staged enforcement
    Explore interactive map
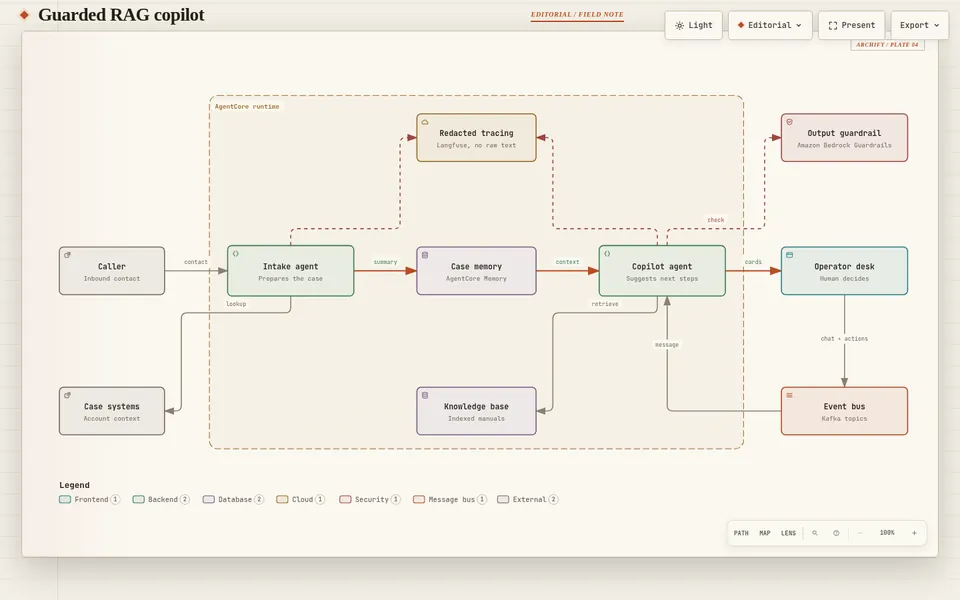
  5. Architecture preview for an intake agent, case memory, a guarded copilot, an event bus to the operator desk, and redacted tracing

    Guarded RAG copilot

    Problem
    A contact-center copilot must ground its suggestions in internal knowledge and case context while the operator stays in control.
    Decision
    An intake agent prepares the case in memory. A copilot on AgentCore retrieves from a knowledge base, checks its output with Bedrock Guardrails, and sends suggestion cards to the operator through an event bus.
    Limitation
    Suggestions are advice, not actions: the operator decides. Retrieval quality and guardrail thresholds need continuous evaluation, and redacted traces trade debugging detail for privacy.
    Technical scope
    Amazon Bedrock AgentCore Runtime and Memory, knowledge-base retrieval, Bedrock Guardrails, Kafka, Langfuse
    Explore interactive map

Certifications

AI Red Teaming

Hack The Box Global Top 10

L4tentNoise

View Hack The Box profile
Hack The Box Global Top 10 achievement badge for L4tentNoise

HTB Certified Offensive AI Expert (COAE)

Hack The Box

Credential ID: HTBCERT-1287C8C6C3

Verify credential

AI Security Write-ups

Four analyses of Hack The Box challenges, focused on defensive lessons and the limits of the evidence.

Experience

  1. BBVA

    AI Security Architect

    Designing AI security architectures and adversarial evaluations across models, data, tools, and human decisions.

  2. Ecoembes

    Machine Learning Engineer

    Built machine-learning systems across computer vision, document NLP, route optimisation, and time-series forecasting, from data preparation to integration and monitoring.

  3. Capgemini

    Data Scientist

    Developed pricing and predictive-analytics models, operational Power BI reporting, and inventory decision support.

Education

  1. UNED

    Bachelor’s Degree in Artificial Intelligence Engineering

    Current undergraduate studies in artificial intelligence engineering.

  2. MIOTI

    Big Data & Data Science Master

    240-hour programme in big data and data science.

  3. MIOTI

    Master in Machine Learning & Deep Learning

    240-hour programme focused on machine learning and deep learning.

Contact

Available for AI security architecture and AI red-team engagements.

Message me on LinkedIn

The AI assistant on this page is a small security exercise of its own: it answers only from public facts, treats visitor messages as untrusted data, is rate-limited, and replies in plain text.